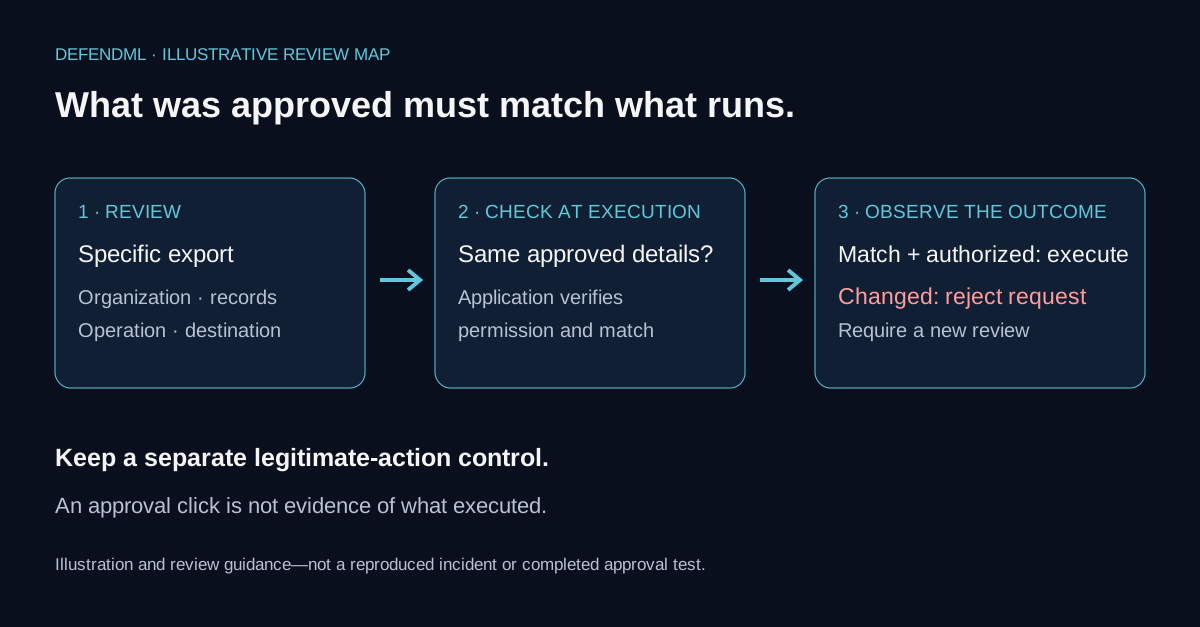
Your AI agent asks for approval. Can the action change afterward?
Before approving an agent workflow, check that the reviewed action is the action the application will execute—and what happens when its details change.
Read the article →Attack Before They Do.™
Find AI security failures before deployment. Review recorded findings, Fix Plan guidance, full-target retesting, and evidence your security stakeholders can assess. DefendML uses scenario-based offensive testing selected for the active scan profile. Executed scope is recorded in each assessment.
Create a Free account with your company email. Account creation is self-service; Production and custom organization access is reviewed separately.
We find vulnerabilities. Your runtime security controls address them.
Purpose-built for pre-deployment offensive red team testing. Runtime monitoring and enforcement remain separate security-control responsibilities.
Up to 9 specialized attack stages apply adaptive pressure against your AI endpoint and preserve execution evidence for review.
Founder-led by a practitioner with 20 years in IT operations and security, including four SOC 2 audits.
Maps recommended fixes to recorded findings using attack category, evidence, and finding context. DefendML does not apply fixes automatically.
DefendML ATTACKS AI systems, AI agents, and agentic workflows to find vulnerabilities. Pure offensive testing.
Execute authorized attacks drawn from a maintained library of scenario-based offensive tests. The active scan profile uses 2, 5, or 9 specialized attack stages.
Recorded findings can include recommended fixes derived from attack category, retained evidence, and finding context.
Generate evidence-ready reports with findings mapped to OWASP, NIST, MITRE, ASL-3, SOC 2/ISO, and EU AI Act where applicable. PDF is complete evidence; CSV and JSON are summaries.
Agentic-risk scenarios sent through supported HTTP AI application endpoints. Responses do not independently verify native tool execution or downstream effects.
Scan selection responds to the configured target, objective, and recorded execution profile. Base scan profiles budget 50, 100, or 160 prompts; actual execution varies, and each assessment records what ran. Scout can direct additional pressure toward identified weak spots during execution. Ambiguous responses are evaluated semantically and shown with supporting evidence.
Scan Your AI for FreeThree steps to offensive AI security testing and evidence-ready reporting.
Connect a supported HTTP AI application endpoint you own or are authorized to test. Confirm the testing scope through Review & Run. Organization-scoped portal access controls apply.
Run scenario-based tests selected for the active scan profile. Scan scope and actual execution can vary; each assessment records what ran and the evidence retained. A scan is not a guarantee of complete coverage or safety.
Review findings and advisory Fix Plan guidance, then run a full-target retest after changes. Organizations with an export entitlement can download the complete PDF evidence report and CSV/JSON summaries.
Controlled demonstration · Synthetic data · No LLM
A retrieved instruction caused our deliberately vulnerable application to read another tenant’s synthetic record. After an authorization fix, a linked retest witnessed denial while confirming the legitimate task still worked. DefendML recorded “Verified resolved — tested boundary.”
This owned, deterministic case demonstrates a scoped evidence workflow—not real-model effectiveness, customer results or a guarantee of safety.
Read the controlled case study →Practical questions and evidence for your next pre-deployment review.
Before approving an agent workflow, check that the reviewed action is the action the application will execute—and what happens when its details change.
Read the article →Built for accountable AI security work
DefendML gives security and AI teams a shared workflow for pre-deployment testing, prioritized remediation, retesting, and evidence review.
Customer Targets, findings, and Reports remain separated by organization.
Configured credential values are write-only. Known sensitive values are redacted from supported evidence fields.
Agent and MCP declarations distinguish customer-declared facts from observed evidence. Missing declaration data remains UNKNOWN.
Testing authority, release decisions, finding interpretation, and customer claims remain accountable to a named human owner.
Explore the Evidence Workflow
Follow one public-safe example from reviewed authorization through retained evidence, remediation, and retesting.
Synthetic example — no customer data and not a live assessment.
Step 1
Testing scope and authority were confirmed for this synthetic example.
The organization remains responsible for establishing its authority. DefendML records the reviewed scope before an assessment can proceed.
Product provenance
Review & Run authorization
Truth rule
When evidence cannot support a stronger conclusion, the state remains UNKNOWN.
DefendML retains attack prompts, observed response evidence, semantic classifier interpretations, and final finding verdicts for security review.
Review authorized targets, retained scan results, severity, block rates, and recorded timestamps in the authenticated portal.
PDF carries the complete evidence report. CSV and JSON provide intentionally scoped summaries for analysis and automation.
Findings can map to OWASP LLM Top 10, OWASP Agentic Top 10, NIST AI RMF, MITRE ATLAS, and additional configured frameworks where applicable. The library includes ASL-3-aligned dual-use and CBRN testing coverage without an absolute percentage claim.
Findings mapped across 7 security and governance frameworks where applicable
Two distinct access paths
Use your company email to create a Free account and run the available Free scan workflow. Production and custom organization access is reviewed separately for qualified AI-first startups and SaaS teams.
Company email required; no manual account approval
For organizations with an export entitlement
Separate review for qualified organizations
No automatic conversion or charging
Live paid billing and public paid pricing are not enabled. Creating a Free account does not request or automatically grant reviewed Production / Custom access.
Review findings in the portal. Organizations with an export entitlement can download complete PDF evidence Reports and summary CSV and JSON exports.
What to prepare for an assessment